AI-Powered Security Analysis Platform

Identify.Assess.Remediate.

CodeShuriken is an enterprise-grade, AI-powered security scanning and vulnerability management platform that helps organizations identify, assess, and remediate security vulnerabilities in their software applications.
Scanning layers
3
Severity levels
5
Alert channels
4
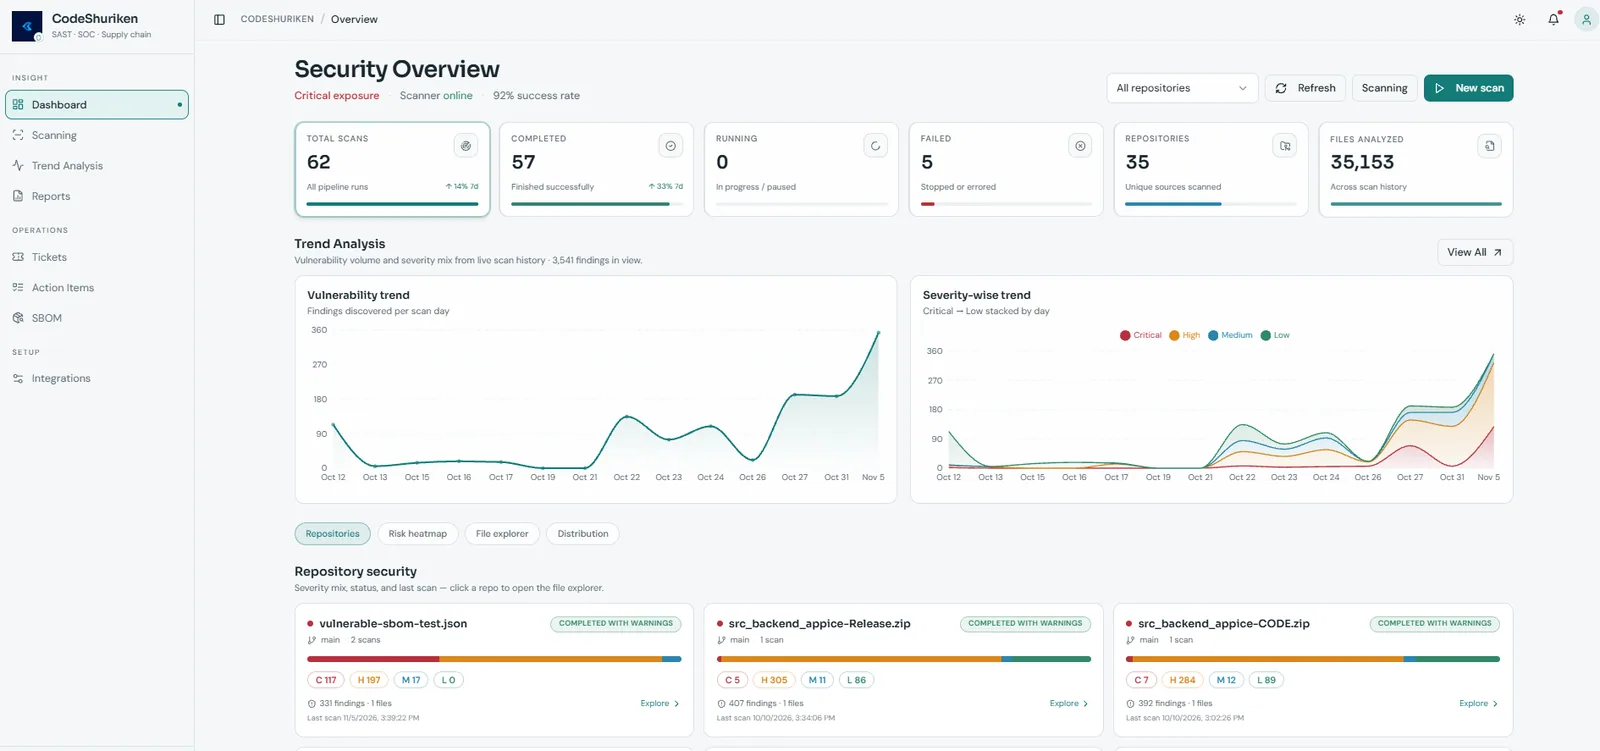
CodeShuriken security overview dashboard with scans, trends, and repository risk
Platform Overview

An intelligent scanning engine, layered by design

A multi-layered scanning approach that combines advanced artificial intelligence with comprehensive reporting, real-time notifications and intuitive dashboards.

Complete Security Audits

Comprehensive analysis of entire codebases including source code, dependencies, and configuration files.

Targeted Vulnerability Scanning

Focuses specifically on application context and code-level security issues.

SBOM Analysis

Deep-dive analysis of all dependencies and third-party packages.
Glowing AI processor cube

Smart scanning, AI-powered analysis

Leverages advanced AI models to understand code context and identify complex vulnerabilities — going beyond pattern matching to detect logic flaws and business logic vulnerabilities.

  • Intelligent file classification for code, manifests and configuration files
  • Handles large codebases through intelligent chunking and parallel processing
  • Resume capability for interrupted scans — picks up exactly where it left off
Core Features

Eight capabilities, one platform

Intelligent Scanning Engine

Multi-layered scanning with real-time progress tracking and detailed status updates.

Comprehensive Reporting

PDF, DOCX, XLSX, CSV and JSON exports with executive summaries and detailed findings.

Dashboard & Visualization

At-a-glance security posture with live vulnerability counters and system health indicators.

Trend Analysis & Historical Tracking

Track vulnerability trends over time and measure the effectiveness of remediation efforts.

SBOM Management

Complete inventory of software components, version tracking and license compliance checking.

Multi-Channel Integration

Instant alerts across Telegram, Discord, email and custom webhooks.

Authentication & Access Control

JWT-based stateless authentication, BCrypt hashing and role-based access control.

Repository Management

Automatic Git cloning, branch-specific scanning and commit-level analysis.

AI Workflow

From repository to remediation

Continuous learning from security research and open source vulnerability databases, applied at every stage of the scan.

  1. 01

    Clone

    Automatically clones and analyzes repositories from version control systems, public or private.

  2. 02

    Classify

    Automatic detection of repository type and structure, language and framework identification.

  3. 03

    Analyze

    Context-aware AI analysis that understands the relationship between different code components.

  4. 04

    Report

    Findings mapped to OWASP, CWE and CVE with CVSS scores and step-by-step remediation guidance.

Severity classification

  • CriticalImmediate threats requiring urgent attention
  • HighSignificant security risks
  • MediumImportant issues that should be addressed
  • LowMinor vulnerabilities and best practice violations
  • InformationalSecurity awareness and improvement suggestions
Product Capabilities

Measure posture, prove progress

Key metrics displayed

  • Total number of security scans performed
  • Active vulnerability count across all repositories
  • Critical and high-severity issue tracking
  • SBOM component analysis with vulnerability mapping
  • Success rate and scan completion statistics

Security metrics over time

  • Track vulnerability trends across multiple time periods
  • Monitor security improvement or degradation
  • Identify patterns in vulnerability discovery
  • Measure effectiveness of remediation efforts

Organization-wide insights

  • Multi-repository comparison views
  • Team and project-level security metrics
  • Compliance posture tracking
  • Security score trending
  • Best and worst performing repositories

Comprehensive visualizations

  • Area charts showing vulnerability trends over time
  • Pie charts for severity distribution
  • Bar charts comparing different repositories
  • Compliance checklist progress tracking
  • Risk assessment by application type
Interactive Dashboard

Complex security data, made actionable

A modern, intuitive dashboard that makes complex security data accessible for teams of all skill levels.
Floating holographic security dashboard panels with charts and metrics
  • At-a-glance overview of organizational security status
  • Live vulnerability counters by severity level
  • Active scan monitoring with progress indicators
  • System health indicators for all services

0

Core platform services

0

Severity classifications

0

Notification channels

0+

Report export formats
Security Intelligence

Supply chain visibility and hardened access

Dependency analysis

  • Complete inventory of all software components and libraries
  • Version tracking for all dependencies
  • Transitive dependency mapping

Vulnerability management

  • Cross-reference dependencies against vulnerability databases
  • Track CVEs associated with specific component versions
  • Recommended version upgrades and patches

Component intelligence

  • Direct vs. transitive dependency classification
  • Security posture scoring for each component
  • Historical vulnerability trends for packages
Glowing security shield hologram

Enterprise-grade access control

  • JWT based stateless authentication
  • BCrypt password hashing with configurable work factors
  • Secure session management with token versioning
  • Role-based access control (Admin, Analyst, Viewer)
  • Encrypted storage of access credentials
  • Automatic SSH key rotation
  • Audit trail for repository access
  • Compliance with data residency requirements
Integrations

Alerts where your team already works

Keep security teams informed with instant notifications across multiple channels, ensuring rapid response to critical vulnerabilities.

Telegram

Direct messages to users via Telegram Bot

Discord

Messages to Discord channels or direct messages

Email

Professional formatted emails via Gmail or custom SMTP

Webhooks

Integration with custom systems and workflows

Real-time delivery

  • Instant alerts when critical vulnerabilities are discovered
  • Scan completion notifications
  • Status updates for long-running analyses
  • Custom trigger-based notifications

Version control

  • Automatic repository cloning from GitHub and other Git platforms
  • Support for both public and private repositories
  • SSH key-based authentication for enhanced security
  • Multiple branch scanning capabilities
  • Commit-level analysis for tracking changes
  • Tag and release scanning
Why CodeShuriken

Seven reasons teams standardize on us

01

AI-Powered Intelligence

Unlike traditional static analysis tools that rely solely on pattern matching, CodeShuriken uses advanced AI models to understand code context, identify complex vulnerabilities, and provide intelligent remediation suggestions.

02

Comprehensive Coverage

From source code vulnerabilities to dependency issues, configuration problems — CodeShuriken provides 360-degree security visibility.

03

Professional Reporting

Generate board-ready reports that communicate security posture to both technical and non-technical stakeholders with professional formatting and clear visualizations.

04

Real-Time Communication

Keep security teams informed with instant notifications across multiple channels, ensuring rapid response to critical vulnerabilities.

05

User-Friendly Interface

Modern, intuitive dashboard that makes complex security data accessible and actionable for teams of all skill levels.

06

Flexible Deployment

Deploy on-premises or in the cloud, with full control over data residency and compliance requirements.

07

Scalable Architecture

Microservices design allows the platform to grow with your organization, from small teams to enterprise-wide deployments.

Use Cases

Built for the way security teams operate

Compliance & Audit

  • Generate compliance reports for SOC 2, ISO 27001, PCI-DSS
  • Track remediation progress for audit requirements
  • SBOM generation for supply chain security
  • Historical evidence of security practices

Third-Party Risk Assessment

  • Evaluate security of vendor code and open-source dependencies
  • Continuous monitoring of supply chain vulnerabilities
  • License compliance verification
  • Component security scoring

Security Program Management

  • Track security metrics across the organization
  • Measure effectiveness of security initiatives
  • Identify training needs based on vulnerability patterns
  • Executive reporting and dashboards

Incident Response

  • Rapid vulnerability assessment during security incidents
  • Historical scan data for forensic analysis
  • Impact assessment across multiple repositories
  • Prioritization of remediation efforts
Reports & Analytics

Board-ready output, engineer-level depth

PDF

Print-ready, executive-level assessment documents

DOCX

Fully editable documents for customization

XLSX / CSV

Spreadsheet exports for deeper analysis

JSON

Integration with other systems

Every report includes

  • Executive Summary with high-level risk assessment
  • Detailed vulnerability breakdown by severity
  • Repository metadata and code statistics
  • File-by-file security analysis
  • Proof-of-concept demonstrations for vulnerabilities
  • Step-by-step remediation guidance
  • OWASP and CWE mappings for compliance
  • CVE references and CVSS scores

Distribution

  • Direct download from the platform
  • Automated delivery via email and messaging channels
  • Archive and versioning of all generated reports
  • Shareable links with access controls

Analysis capabilities

Week-over-week and month-over-month comparisonsIdentify recurring vulnerability patternsMeasure time-to-remediation metricsTrack security debt accumulationGenerate actionable improvement recommendations
CodeShuriken logo

Actionable security insights for your entire codebase

Deploy on-premises or in the cloud, with full control over data residency and compliance requirements.